

Ports no longer only face threats at sea or on land, as a cyberattack can paralyze the movement of cranes , stop the transport of containers and cause disruptions in supply chains, with losses of millions and stranded goods.
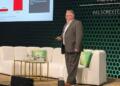
This was explained by Rodrigo Díaz, an international expert in maritime and port cybersecurity, who said that the increasing digitalization of port terminals expands the exposure and makes cybersecurity a determining factor to guarantee the continuity of trade.
Díaz mentioned the case of Colonial Pipeline in the United States, which in 2021 suspended its operations for six days due to fears that a cyberattack would reach its control systems, as well as the NotPetya attack in 2017, which affected the shipping company Maersk and caused an operational disruption of approximately 24 hours, while the recovery of its operations took more than 10 days, with estimated losses of 300 million dollars.

He asserted that these events demonstrate that critical infrastructures are exposed to threats that can have far greater economic and operational consequences than the initial technological damage.
He considered that one of the main risks lies in the interconnection between ports , suppliers, among others, even if a terminal has protection mechanisms, its external access points can become vulnerable.
“The port operates with an ecosystem that is the weakest link,” he noted during the Cybersecurity and Digital Resilience panel: Protecting Connected Global Logistics Supply Chains 2025, organized by the World Organization of Logistics Cities and Platforms.
Therefore, he mentioned that the role of artificial intelligence is to identify abnormal behaviors, analyze large volumes of information, and detect threats before they reach critical systems.
He explained that, according to an IBM report, the average cost of a security breach reached $5.5 million, while in the transportation sector it was approximately $4.5 million. He also indicated that 61% of breaches in the transportation sector were due to malicious attacks.
Rodrigo Díaz emphasized that companies must differentiate between information technology systems and operational technology systems, because the latter control physical equipment and tend to have longer life cycles, making them difficult to update.
He also warned that small and medium-sized enterprises are not exempt; even a micro-enterprise can fall victim to an information kidnapping whose economic demands jeopardize its survival.
Therefore, he said that cybersecurity must be considered from the beginning of any automation and digitization project, since protecting the infrastructure, training staff and having response protocols is essential to prevent a computer incident from becoming a supply crisis and affecting logistics.
Comment and follow us on LinkedIn: @Evangelina del Toro / @GrupoT21